
CA1-005 Sample Questions & Answers
Automation, orchestration and advanced cryptography carry the heaviest weight, alongside cloud security architecture built on zero trust, governance frameworks and program documentation, and incident response with security monitoring.
Launch the full CA1-005 simulator →Showing 10 of 20 free samples.
- Question 1Intermediate
A manufacturing plant is updating its IT services. During discussions, the senior management team created the following list of considerations:• Staff turnover is high and seasonal.• Extreme conditions often damage endpoints.• Losses from downtime must be minimized.• Regulatory data retention requirements exist.Which of the following best addresses the considerations? A.Establishing further environmental controls to limit equipment damageB.Using a non-persistent virtual desktop interface with thin clientsC.Deploying redundant file servers and configuring database journalingD.Maintaining an inventory of spare endpoints for rapid deployment
Show answer & explanation
Correct answer: B
- Question 2Intermediate
A company runs a DAST scan on a web application. The tool outputs the following recommendations:• Use Cookie prefixes.• Content Security Policy - SameSite=strict is not set.Which of the following vulnerabilities has the tool identified? A.RCEB.XSSC.CSRFD.TOCTOU
Show answer & explanation
Correct answer: C
- Question 3IntermediateSelect 2
A company hired an email service provider called my-email.com to deliver company emails. The company started having several issues during the migration. A security engineer is troubleshooting and observes the following configuration snippet:Which of the following should the security engineer modify to fix the issue? (Choose two.) A.The email CNAME record must be changed to a type A record pointing to 192.168.1.11B.The TXT record must be changed to "v=dmarc ip4:192.168.1.10 include:my-email.com ~all"C.The srv01 A record must be changed to a type CNAME record pointing to the email serverD.The email CNAME record must be changed to a type A record pointing to 192.168.1.10E.The TXT record must be changed to "v=dkim ip4:192.168.1.11 include :my-email.com ~all"F.The TXT record must be changed to "v=spf ip4:192.168.1.10 include :my-email.com ~all"G.The srv01 A record must be changed to a type CNAME record pointing to the web01 server
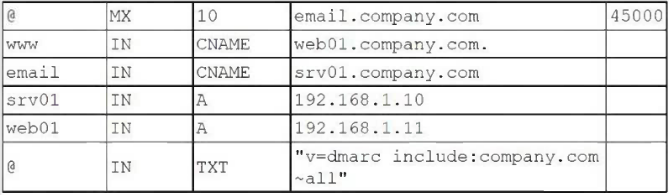
Show answer & explanation
Correct answers: D, F
- Question 4Intermediate
Governance, Risk and Compliance · Compliance Management
A government contractor is preparing for a Cybersecurity Maturity Model Certification (CMMC) Level 2 assessment. The security architect needs to design a solution that enforces data residency for Controlled Unclassified Information (CUI) within a multi-tenant cloud environment, ensuring that data is processed and stored exclusively within U.S. sovereign boundaries. Which cloud architecture and service model would be the MOST appropriate choice to meet this stringent compliance requirement?
Show answer & explanation
Correct answer: B
Government community clouds like AWS GovCloud and Azure Government are specifically designed to meet the stringent compliance and data sovereignty requirements of U.S. government agencies and contractors. These environments are physically and logically isolated from the public cloud, are managed exclusively by vetted U.S. persons, and provide the necessary controls to handle regulated data like CUI, making them the most appropriate choice for CMMC Level 2 and higher.
- Question 5Intermediate
Security Operations · Threat Hunting
A SOC manager is developing a threat hunting program. The initial hunts will be based on Tactics, Techniques, and Procedures (TTPs) from the MITRE ATT&CK framework. The manager wants to create a structured, repeatable process for the hunt team. Which of the following represents the most logical and effective sequence of steps for a hypothesis-driven threat hunt?
Show answer & explanation
Correct answer: C
This is the correct sequence for a structured, hypothesis-driven threat hunt. The process begins by forming a specific hypothesis (e.g., 'An adversary is using PowerShell for lateral movement'). Next, the team gathers relevant intelligence and collects data from sources like EDR, SIEM, and network logs. They then investigate this data to find patterns confirming or denying the hypothesis. Finally, if the hunt is successful, the findings are used to create automated detection rules (enrichment) to catch this activity in the future.
- Question 6Intermediate
Security Architecture · Cloud Architecture
A financial institution is deploying a new mobile banking application that will be hosted in a public cloud environment. The security architecture must prevent common web application vulnerabilities, including injection attacks and cross-site scripting (XSS), while also protecting against credential stuffing and application-layer DDoS attacks. The solution must be scalable and managed as a service to reduce operational overhead. Which of the following security services should be placed in front of the application load balancers to meet all these requirements?
Show answer & explanation
Correct answer: B
A cloud-native WAF is the most appropriate solution. It operates at the application layer (Layer 7) to inspect HTTP/S traffic and can detect and block common attacks like SQL injection and XSS using managed rules (e.g., OWASP Top 10). Advanced WAF services also include bot protection to mitigate credential stuffing and rate-based rules to defend against application-layer DDoS attacks. As a managed cloud service, it meets the requirements for scalability and reduced operational overhead.
- Question 7AdvancedSelect 2
Security Engineering · Automation and Orchestration
A large enterprise is struggling with inconsistent security configurations across its multi-cloud environment, leading to compliance drift and security gaps. The DevSecOps team wants to automate the deployment and validation of security controls to ensure a consistent baseline. Which of the following technologies should be implemented to achieve this goal? (Select TWO).
Show answer & explanation
Correct answers: A, C
IaC tools (like Terraform, CloudFormation, or Ansible) allow the team to define infrastructure and its configuration in code. This enables the automated, repeatable, and consistent deployment of resources, including security controls like firewall rules, IAM policies, and network configurations, across multiple environments.
PaC frameworks (like Open Policy Agent - OPA) allow security and compliance policies to be defined as code. These policies can be automatically checked against IaC templates before deployment and can continuously validate deployed resources, ensuring they adhere to the required security baseline and preventing configuration drift.
- Question 8Advanced
Security Operations · Incident Response
A security analyst is performing a forensic investigation on a compromised Linux server. The analyst has created a disk image and needs to reconstruct the timeline of attacker activity. The attacker cleared the bash history and modified file timestamps. Which of the following forensic artifacts would be MOST valuable for recreating a chronological sequence of executed commands and system events?
Show answer & explanation
Correct answer: C
The systemd journal (accessed via journalctl) provides a centralized, indexed, and tamper-evident binary logging system on modern Linux distributions. It captures a vast range of events, including service startups/shutdowns, kernel messages, user logins, and commands executed via sudo, all with high-precision timestamps. Unlike plain-text logs, it is more difficult for an attacker to selectively manipulate, making it the most reliable and comprehensive source for reconstructing a chronological event timeline.
- Question 9Beginner
Security Architecture · Zero Trust Architecture
True or False: In a Zero Trust architecture, once a user has authenticated with multi-factor authentication (MFA) at the network edge, their connection is considered trusted for the duration of the session and they are allowed access to all internal resources permitted by their role.
Show answer & explanation
Correct answer: B
The statement is false. A core principle of Zero Trust is 'never trust, always verify.' Trust is not granted for a session based on a single authentication event at the perimeter. Instead, trust is continuously evaluated, and every access request to a resource must be individually authenticated and authorized based on identity, device posture, and other contextual signals, regardless of network location.
- Question 10Advanced
Governance, Risk and Compliance · Risk Management
A risk analyst is performing a quantitative risk assessment for an e-commerce platform. The company has determined that a successful DDoS attack would result in an estimated $200,000 of lost revenue and recovery costs. Based on historical data and threat intelligence, an attack of this magnitude is expected to occur once every four years. The company is considering a DDoS mitigation service that costs $60,000 per year and is expected to reduce the likelihood of a successful attack by 90%. What is the Return on Security Investment (ROSI) for this mitigation service?
Show answer & explanation
Correct answer: C
- Calculate ALE before mitigation: SLE = $200,000. ARO = 1/4 years = 0.25. ALE = $200,000 * 0.25 = $50,000.
- Calculate ALE after mitigation: The mitigation reduces risk by 90%, so the remaining risk is 10%. New ALE = $50,000 * 0.10 = $5,000.
- Calculate risk mitigated: $50,000 (old ALE) - $5,000 (new ALE) = $45,000.
- Calculate ROSI: ROSI = (Risk Mitigated - Cost of Control) / Cost of Control. ROSI = ($45,000 - $60,000) / $60,000 = -$15,000 / $60,000 = -0.25 or -25%. The investment results in a net loss.
Ready for the real thing?
The full CA1-005 simulator has every exam-style question, timed mode, and instant scoring.