
ECSAv10 Sample Questions & Answers
Core networking, security controls, and Windows/Linux basics take the biggest share, framed by scoping and OSINT methods, social-engineering testing, network checks from outside, inside, and the perimeter, web, database, wireless, and cloud testing, and reporting.
Launch the full ECSAv10 simulator →Showing 10 of 20 free samples.
- Question 1
Steven is performing a wireless network audit. As part of the engagement, he is trying to crack a WPA-PSK key. Steven has captured enough packets to run aircrack-ng and discover the key, but aircrack-ng did not yield any result, as there were no authentication packets in the capture.
Which of the following commands should Steven use to generate authentication packets?
Show answer & explanation
Correct answer: A
A
- Question 2
Sam was asked to conduct penetration tests on one of the client’s internal networks. As part of the testing process, Sam performed enumeration to gain information about computers belonging to a domain, list of shares on the individual hosts in the network, policies and passwords.
Identify the enumeration technique.
Show answer & explanation
Correct answer: B
B
- Question 3
Jason is working on a pen testing assignment. He is sending customized ICMP packets to a host in the target network. However, the ping requests to the target failed with “ICMP Time Exceeded Type = 11 error messages.
What can Jason do to overcome this error?
Show answer & explanation
Correct answer: C
C
- Question 4
Joseph, a penetration tester, was hired by Xsecurity Services. Joseph was asked to perform a pen test on a client’s network. He was not provided with any information about the client organization except the company name.
Identify the type of testing Joseph is going to perform for the client organization?
Show answer & explanation
Correct answer: B
B
- Question 5
An organization deployed Microsoft Azure cloud services for running their business activities. They appointed Jamie, a security analyst for performing cloud penetration testing. Microsoft prohibits certain tests to be carried out on their platform.
Which of the following penetration testing activities Jamie cannot perform on the Microsoft Azure cloud service?
Show answer & explanation
Correct answer: B
B
- Question 6
Sandra, a wireless network auditor, discovered her client is using WEP. To prove the point that the WEP encryption is very weak, she wants to decrypt some WEP packets. She successfully captured the WEP data packets, but could not reach the content as the data is encrypted.
Which of the following will help Sandra decrypt the data packets without knowing the key?
Show answer & explanation
Correct answer: B
B
- Question 7
Peter, a disgruntled ex-employee of Zapmaky Solutions Ltd., is trying to jeopardize the company’s website http://zapmaky.com. He conducted the port scan of the website by using the Nmap tool to extract the information about open ports and their corresponding services. While performing the scan, he recognized that some of his requests are being blocked by the firewall deployed by the IT personnel of Zapmaky and he wants to bypass the same. For evading the firewall, he wanted to employ the stealth scanning technique which is an incomplete TCP three-way handshake method that can effectively bypass the firewall rules and logging mechanisms.
Which if the following Nmap commands should Peter execute to perform stealth scanning?
Show answer & explanation
Correct answer: A
A
- Question 8
Richard, a penetration tester was asked to assess a web application. During the assessment, he discovered a file upload field where users can upload their profile pictures. While scanning the page for vulnerabilities, Richard found a file upload exploit on the website. Richard wants to test the web application by uploading a malicious PHP shell, but the web page denied the file upload. Trying to get around the security, Richard added the ‘jpg’ extension to the end of the file. The new file name ended with ‘.php.jpg’. He then used the Burp suite tool and removed the ‘jpg’’ extension from the request while uploading the file. This enabled him to successfully upload the PHP shell.
Which of the following techniques has Richard implemented to upload the PHP shell?
Show answer & explanation
Correct answer: D
D
- Question 9
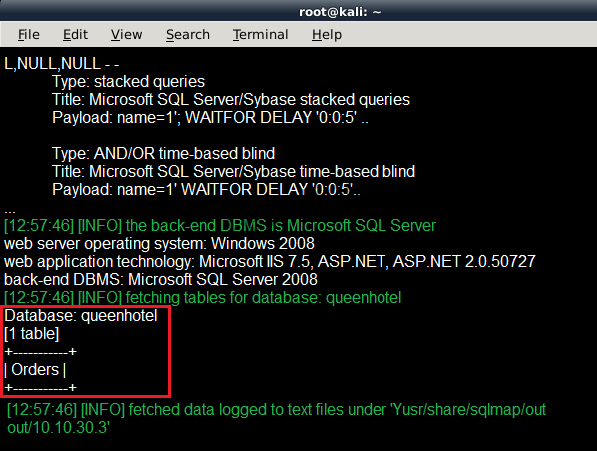
Richard is working on a web app pen testing assignment for one of his clients. After preliminary information, gathering and vulnerability scanning Richard runs the SQLMAP tool to extract the database information.
Which of the following commands will give Richard an output as shown in the screenshot?
Show answer & explanation
Correct answer: A
A
- Question 10
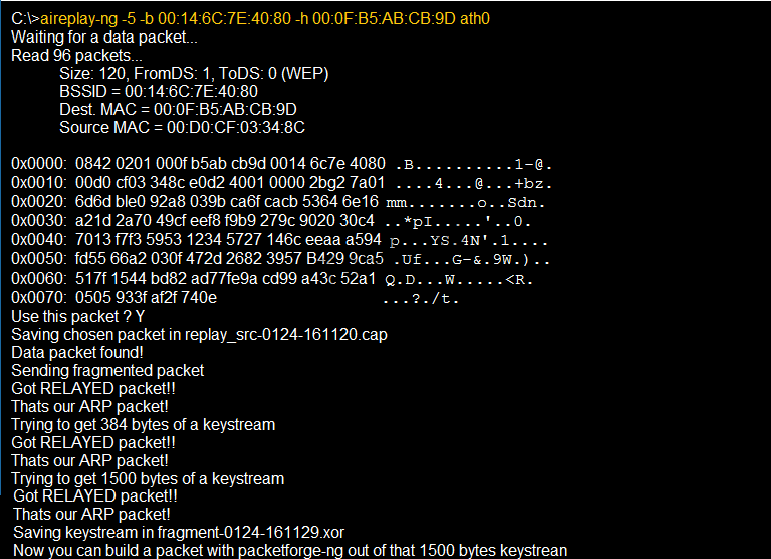
Identify the PRGA from the following screenshot:
Show answer & explanation
Correct answer: A
A
Ready for the real thing?
The full ECSAv10 simulator has every exam-style question, timed mode, and instant scoring.