
NSE4_FGT-6.4 Sample Questions & Answers
Firewall policy and NAT configuration ties with SSL inspection, web filtering, and application control for the top weighting, next to initial setup with VDOMs and the Security Fabric, authentication and FSSO identity policies, SD-WAN routing, and VPNs.
Launch the full NSE4_FGT-6.4 simulator →Showing 6 of 12 free samples.
- Question 1Select 3
Which three security features require the intrusion prevention system (IPS) engine to function? (Choose three.)
Show answer & explanation
Correct answers: A, C, E
A, C, E
A, C, E
A, C, E
- Question 2
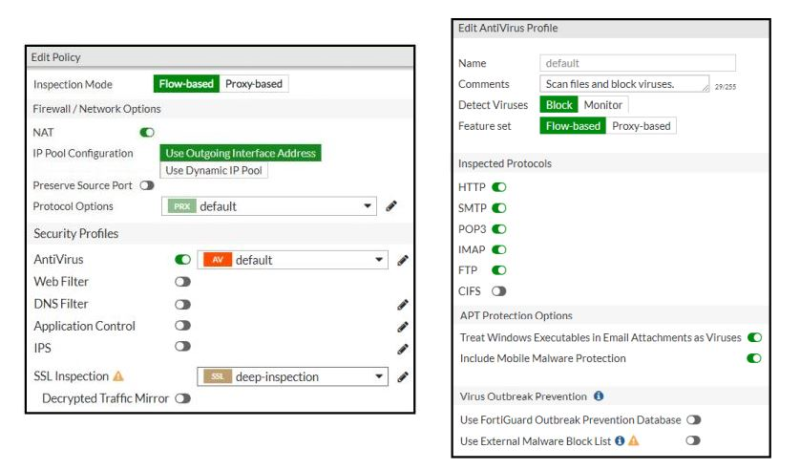
Refer to the exhibits to view the firewall policy (Exhibit A) and the antivirus profile (Exhibit B).
Exhibit A
Exhibit B
Which statement is correct if a user is unable to receive a block replacement message when downloading an infected file for the first time?
Show answer & explanation
Correct answer: C
C
- Question 3
Which Security rating scorecard helps identify configuration weakness and best practice violations in your network?
Show answer & explanation
Correct answer: C
- Question 4
What devices form the core of the security fabric?
Show answer & explanation
Correct answer: C
- Question 5
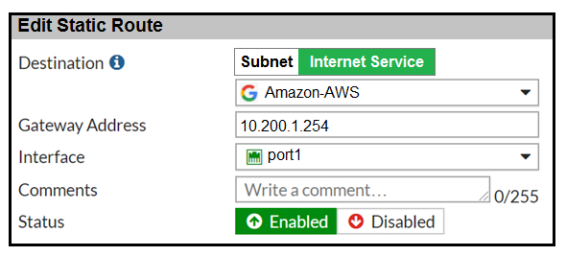
Refer to the exhibit, which contains a static route configuration.
An administrator created a static route for Amazon Web Services.
What CLI command must the administrator use to view the route?
Show answer & explanation
Correct answer: D
- Question 6
An administrator needs to configure VPN user access for multiple sites using the same soft FortiToken. Each site has a FortiGate VPN gateway.
What must an administrator do to achieve this objective?
Show answer & explanation
Correct answer: C
C
Ready for the real thing?
The full NSE4_FGT-6.4 simulator has every exam-style question, timed mode, and instant scoring.