
70-744 Sample Questions & Answers
Hardening the server with disk encryption and patching ties with managing privileged identities through ESAE for the top weight, alongside securing virtualization with Shielded VMs, firewall rules, threat detection with ATA, and workload security.
Launch the full 70-744 simulator →Showing 10 of 20 free samples.
- Question 1Intermediate
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.After you answer a question in this sections, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.Your network contain an Active Directory domain named contoso.com. The domain contains a computer named Computer1 that runs Windows 10. Computer1 connects to a home network and a corporate network.The corporate network uses the 172.16.0.0/24 address space internally.Computer1 runs an application named App1 that listens to port 8080.You need to prevent connections to App1 when Computer1 is connected to the home network.Solution: From Windows Firewall in the Control Panel, you add an application and allow the application to communicate through the firewall on a Private network.Does this meet the goal? A.YesB.No
Show answer & explanation
Correct answer:
- Question 2Intermediate
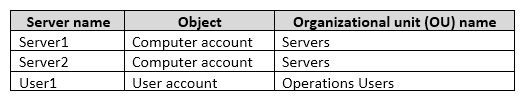
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.After you answer a question in this sections, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.Your network contains an Active Directory domain named contoso.com. All servers run Windows Server 2016. All client computers run Windows 10.The relevant objects in the domain are configured as shown in the following table.You need to assign User1 the right to restore files and folders on Server1 and Server2.Solution: You create a Group Policy object (GPO), you link the GPO to the Servers OU, and then you modify the Users Rights Assignment in the GPO.Does this meet the goal? A.YesB.No
Show answer & explanation
Correct answer:
- Question 3Intermediate
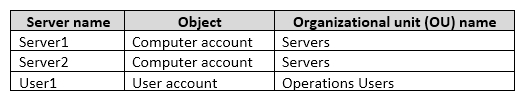
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.After you answer a question in this sections, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.Your network contains an Active Directory domain named contoso.com. All servers run Windows Server 2016. All client computers run Windows 10.The relevant objects in the domain are configured as shown in the following table.You need to assign User1 the right to restore files and folders on Server1 and Server2.Solution: You add User1 to the Backup Operators group in contoso.com.Does this meet the goal? A.YesB.No
Show answer & explanation
Correct answer: A
- Question 4Intermediate
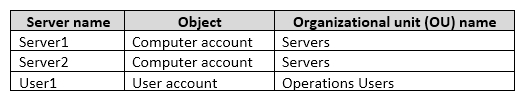
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.After you answer a question in this sections, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.Your network contains an Active Directory domain named contoso.com. All servers run Windows Server 2016. All client computers run Windows 10.The relevant objects in the domain are configured as shown in the following table.You need to assign User1 the right to restore files and folders on Server1 and Server2.Solution: You create a Group Policy object (GPO), link it to the Operations Users OU, and modify the Users Rights Assignment in the GPO.Does this meet the goal? A.YesB.No
Show answer & explanation
Correct answer:
- Question 5Intermediate
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.After you answer a question in this sections, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.Your network contains an Active Directory domain named contoso.com. The domain contains multiple Hyper-V hosts.You need to deploy several critical line-of-business applications to the network to meet the following requirements:✑ The resources of the applications must be isolated from the physical host.✑ Each application must be prevented from accessing the resources of the other applications.✑ The configurations of the applications must be accessible only from the operating system that hosts the application.Solution: You deploy a separate Windows container for each application.Does this meet the goal? A.YesB.No
Show answer & explanation
Correct answer: A
- Question 6Advanced
Manage Privileged Identities (25-30%) · Implement Privileged Access Workstations (PAWs) and User Rights Assignments
A financial institution is deploying a new Active Directory administrative forest based on the Enhanced Security Administrative Environment (ESAE) model. To manage the production forest, administrators will use Privileged Access Workstations (PAWs). A critical security requirement is to prevent any credential theft from RDP sessions initiated from the PAWs to production servers. Which Group Policy setting must be configured and enforced on the production servers to meet this requirement?
Show answer & explanation
Correct answer: B
Remote Credential Guard prevents credentials from being transmitted to the target server during an RDP session by redirecting Kerberos requests back to the client. This is the specific feature designed to protect against credential theft on the remote host, making it essential for PAW implementations.
- Question 7Intermediate
Manage Privileged Identities (25-30%) · Implement Just-Enough-Administration (JEA)
A security administrator has implemented a Just-Enough-Administration (JEA) endpoint on a member server to allow junior operators to restart specific services. After deployment, operators report that they can connect to the JEA endpoint but receive an error when trying to run
Restart-Service. The administrator has verified the Role Capability file (.psrc) correctly listsRestart-Servicein theVisibleCmdletssection. What is the most likely cause of this issue?Show answer & explanation
Correct answer: B
The
Restart-Servicecmdlet often depends on other cmdlets, such asGet-Service, to function correctly (e.g., to find the service to restart). If a dependency cmdlet is not also made visible in the Role Capability file, the primary cmdlet will fail. This is a common oversight in JEA configuration. - Question 8Advanced
Implement Server Hardening Solutions (25-30%) · Protect credentials
You are hardening a fleet of Windows Server 2016 machines that handle sensitive data. You have enabled Credential Guard via Group Policy. To verify the deployment, you run
Get-CimInstance -ClassName Win32_DeviceGuard -Namespace root\Microsoft\Windows\DeviceGuard. The output forSecurityServicesRunningincludesCredential Guard, but theVirtualizationBasedSecurityStatusis1(Disabled). What is the most likely reason for this discrepancy?Show answer & explanation
Correct answer: C
Credential Guard relies on Virtualization-Based Security (VBS). A key prerequisite for VBS is that the hardware must have Secure Boot enabled in the UEFI firmware. If Secure Boot is disabled, VBS cannot start, and consequently, Credential Guard will not be fully operational, leading to the
VirtualizationBasedSecurityStatusof 'Disabled' even if the service is configured. - Question 9Intermediate
Implement Server Hardening Solutions (25-30%) · Protect credentials
A manufacturing company uses a custom legacy application that authenticates using NTLMv1. As part of a security hardening initiative, you are tasked with preventing the use of NTLM on all servers except for the specific server hosting this legacy application. You need to implement a solution using Group Policy that allows for an exception. Which policy should you configure?
Show answer & explanation
Correct answer: D
This specific policy is designed for exactly this scenario. It allows an administrator to enforce a domain-wide NTLM restriction policy (like 'Deny all') while creating an explicit list of servers that are exempt from the restriction, enabling legacy applications to continue functioning on those specific machines.
- Question 10IntermediateSelect 2
Secure a Virtualization Infrastructure (5-10%) · Implement a Guarded Fabric solution
You are deploying a Guarded Fabric infrastructure. You have decided to use TPM-trusted attestation for the highest level of security. After configuring the Host Guardian Service (HGS) and adding the TPM identifiers for your Hyper-V hosts, you discover that one of the hosts consistently fails the attestation process. All other hosts are working correctly. Which of the following items should you investigate FIRST on the failing host to resolve the issue? (Select TWO).
Show answer & explanation
Correct answers: A, C
TPM-trusted attestation validates the host's boot chain, including the Code Integrity policy. If the policy on the failing host has been modified or is different from the baseline configured in HGS, attestation will fail.
TPM attestation measures the entire boot process to ensure it is secure. A fundamental part of this is Secure Boot. If Secure Boot has been disabled or tampered with on the failing host, the measured boot log will not match the baseline, causing attestation to fail.
Ready for the real thing?
The full 70-744 simulator has every exam-style question, timed mode, and instant scoring.