
300-730 Sample Questions & Answers
Remote-access VPN types such as AnyConnect IKEv2, SSL and clientless make up the biggest chunk, alongside site-to-site designs built with GETVPN, DMVPN and FlexVPN, ASDM and CLI-based IPsec troubleshooting, and overall VPN architecture decisions.
Launch the full 300-730 simulator →Showing 8 of 17 free samples.
- Question 1IntermediateSelect 2
Which two changes should be made in order to migrate from DMVPN Phase 2 to Phase 3 when EIGRP is configured? (Choose two.)
Show answer & explanation
Correct answers: C, D
In DMVPN Phase 2 with EIGRP, the hub runs no ip next-hop-self eigrp so that every spoke learns the other spokes' networks with the remote spoke as next hop. Phase 3 removes that need: Cisco's NHRP shortcut-switching guide says spokes can use summarized routes whose next hop is the hub's tunnel address and still build spoke-to-spoke tunnels, because NHRP installs shortcut routes after the hub sends an NHRP redirect. The migration therefore adds ip nhrp redirect on the hub tunnel, so the hub signals spokes when traffic enters and leaves the same tunnel, and returns EIGRP next-hop-self to its default on the hub so the hub can advertise itself as next hop, including summaries. Cisco's Phase 3 example hub has ip nhrp redirect and ip summary-address eigrp and no 'no ip next-hop-self eigrp'. Disabling next-hop-self is the Phase 2 setting, not a migration step. The spokes need ip nhrp shortcut to act on the redirects, so adding shortcuts on the hub, or redirects on the spokes in place of the hub, does not give the hub the redirect role Phase 3 depends on. Sources: Cisco, 'Shortcut Switching Enhancements for NHRP in DMVPN Networks' (IOS XE 16.9); Cisco, 'Configure Phase-3 Hierarchical DMVPN with Multi-Subnet Spokes'.
In DMVPN Phase 2 with EIGRP, the hub runs no ip next-hop-self eigrp so that every spoke learns the other spokes' networks with the remote spoke as next hop. Phase 3 removes that need: Cisco's NHRP shortcut-switching guide says spokes can use summarized routes whose next hop is the hub's tunnel address and still build spoke-to-spoke tunnels, because NHRP installs shortcut routes after the hub sends an NHRP redirect. The migration therefore adds ip nhrp redirect on the hub tunnel, so the hub signals spokes when traffic enters and leaves the same tunnel, and returns EIGRP next-hop-self to its default on the hub so the hub can advertise itself as next hop, including summaries. Cisco's Phase 3 example hub has ip nhrp redirect and ip summary-address eigrp and no 'no ip next-hop-self eigrp'. Disabling next-hop-self is the Phase 2 setting, not a migration step. The spokes need ip nhrp shortcut to act on the redirects, so adding shortcuts on the hub, or redirects on the spokes in place of the hub, does not give the hub the redirect role Phase 3 depends on. Sources: Cisco, 'Shortcut Switching Enhancements for NHRP in DMVPN Networks' (IOS XE 16.9); Cisco, 'Configure Phase-3 Hierarchical DMVPN with Multi-Subnet Spokes'.
- Question 2Intermediate
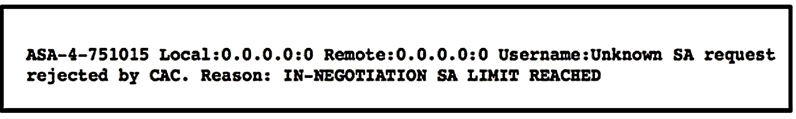
Refer to the exhibit. A customer cannot establish an IKEv2 site-to-site VPN tunnel between two Cisco ASA devices. Based on the syslog message, which action brings up the VPN tunnel? A.Reduce the maximum SA limit on the local Cisco ASA.B.Increase the maximum in-negotiation SA limit on the local Cisco ASA.C.Remove the maximum SA limit on the remote Cisco ASA.D.Correct the crypto access list on both Cisco ASA devices.
Show answer & explanation
Correct answer:
- Question 3IntermediateSelect 2
Which two parameters help to map a VPN session to a tunnel group without using the tunnel-group list? (Choose two.)
Show answer & explanation
Correct answers: A, D
- Question 4Intermediate
Which method dynamically installs the network routes for remote tunnel endpoints? A.policy-based routingB.CEFC.reverse route injectionD.route filtering
Show answer & explanation
Correct answer: C
- Question 5Advanced
Site-to-site Virtual Private Networks on Routers and Firewalls · Implement FlexVPN
A network architect is designing a high-availability VPN solution for a financial institution. The design requires a FlexVPN hub-and-spoke topology where the spokes must authenticate the hub using a digital certificate, but the hub must authenticate spokes using EAP-TLS to integrate with an existing RADIUS infrastructure. Which specific IKEv2 configuration construct allows for asymmetric authentication methods between the peers?
Show answer & explanation
Correct answer: C
IKEv2 supports asymmetric authentication, meaning the two peers do not need to use the same method to authenticate each other. In this scenario, the hub configures
authentication local rsa-sigto present a certificate to the spoke, andauthentication remote eapto demand EAP authentication from the spoke. - Question 6Intermediate
Troubleshooting using ASDM and CLI · Troubleshoot DMVPN
A senior engineer is troubleshooting a DMVPN Phase 3 network where spoke-to-spoke tunnels are failing to establish. The hub router is correctly rewriting the next-hop, but the spokes are not installing the shortcut routes. Which command should be verified on the spoke routers' tunnel interfaces?
Show answer & explanation
Correct answer: B
In DMVPN Phase 3, the
ip nhrp shortcutcommand is required on the spoke routers. This command enables the spoke to accept NHRP redirect messages from the hub and to resolve the NBMA address of the target spoke to install a CEF shortcut (specific route) for direct communication. - Question 7Intermediate
Remote access VPNs · Implement Clientless SSL VPN
While configuring a Cisco ASA for clientless SSL VPN, an administrator needs to ensure that users can access an internal file server using the CIFS protocol without requiring a Java plug-in. Which feature should be configured to meet this requirement?
Show answer & explanation
Correct answer: D
The ASA Clientless SSL VPN portal includes a native file browser that supports CIFS (Common Internet File System). This allows users to browse file shares directly through the web portal interface using HTML rendering, without requiring Java or ActiveX plug-ins.
- Question 8IntermediateSelect 2
Troubleshooting using ASDM and CLI · Troubleshoot FlexVPN
A network engineer observes that IKEv2 negotiation between a FlexVPN hub and spoke is failing. The debug output shows the error
IKEv2-ERROR: Policy not found. Which two actions should be taken to resolve this issue? (Select TWO)Show answer & explanation
Correct answers: D, E
The 'Policy not found' error in IKEv2 typically indicates that the receiver could not find an IKEv2 profile that matches the incoming request. This matching is primarily done via the
match identitycommands.While 'Policy not found' points to profile selection, if no valid IKEv2 proposal exists (or the default smart defaults don't match), the negotiation cannot proceed to a point where a policy is fully established. However, profile matching is the most direct cause of this specific error text.
Ready for the real thing?
The full 300-730 simulator has every exam-style question, timed mode, and instant scoring.